Model provider
Runs the model and its provider-native safety controls.
 Koreshield
Stop untrusted customer content from becoming trusted instructions inside your AI workflow.
Find Koreshield on Product Hunt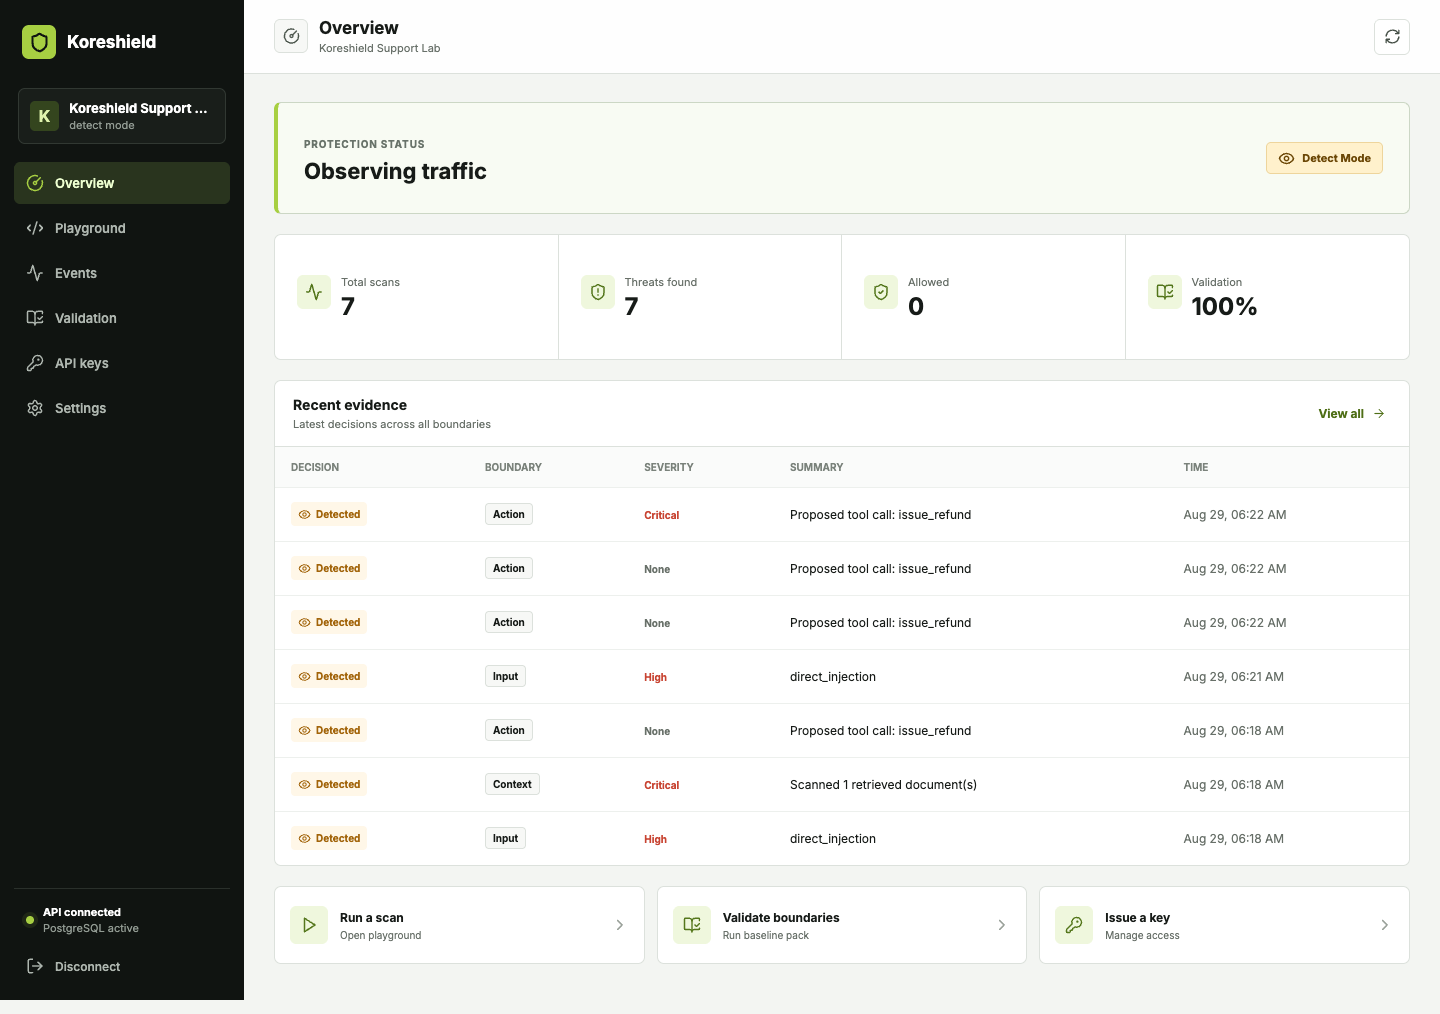
Safety tooling cannot automatically know a customer’s identity, your approval limits, or whether an agent should change an order or account.
Runs the model and its provider-native safety controls.
Checks customer input, retrieved context, and proposed actions before the workflow trusts or executes them.
Remains responsible for identity, authorization, approval rules, tenant isolation, and execution.
Koreshield evaluates each boundary independently and records the reason for every decision.
Inspect messages, attachments, and externally controlled text before model execution.
Keep poisoned tickets, CRM notes, and RAG documents from inheriting system authority.
Evaluate tool calls against trust, approval, and authorization limits before execution.
Begin with live traffic in detect mode. Review expected behavior and false positives, then enable enforcement when the fallback path is ready.
POST /v1/rag/scanX-API-Key: ks_live_••••••••{"source": "ticket_comment","trust_level": "untrusted"}→ decision: detected→ severity: critical→ mode: detectKoreshield should prove itself against your support workflow before any request is blocked.
Run the FastAPI security service with PostgreSQL and connect from the hosted console or your own support infrastructure.
Start free evaluationSee how the same runtime checkpoints apply when an agent can change an order, access a private workspace, or touch sensitive financial information.